Five Firewall Habits That Quietly Open Your Network
- [email protected] (Route XP)
- 508 views
Stale rules, flat internal networks, exposed admin ports, uninspected TLS and silent logs are the firewall gaps to audit before attackers find them.

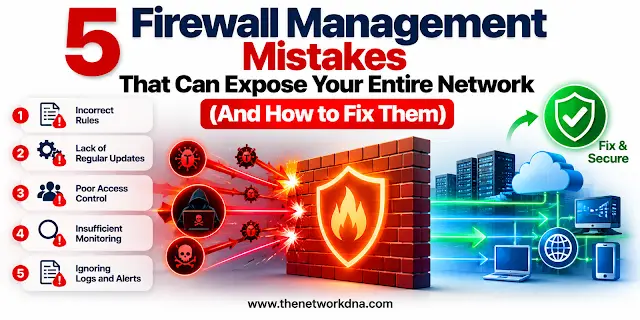
Read the post-incident reports from a serious intrusion and you'll often see the same thing. The victim rarely lacked security spend. They had enterprise firewalls, threat intelligence feeds, intrusion prevention and high-availability pairs. The attackers still got in, mapped the directory servers and moved data out without a single automated block firing.
So why do expensive stacks fail when it counts? My read is that a firewall isn't a purchase you finish. It's an operational discipline. Mergers, emergency changes made late on a Friday, cloud migrations and staff turnover slowly turn a clean rulebase into a tangle of implicit trust. Small administrative shortcuts pile up until they become exposure across the whole estate.
Why misconfiguration gets past good hardware
Firewall misconfiguration causes breaches by opening paths around the controls you think are in place. The usual culprits are overly permissive any-any rules, administrative interfaces reachable from the internet, TLS decryption switched off, and internal zones that trust everything inside them. Together they let an attacker sidestep deep packet inspection, reach an unpatched edge service and then move sideways without resistance.
Attackers rarely bother with custom zero-day exploits when a misconfigured access list hands them a way in. Automated scanners sweep public address space continuously, looking for forgotten remote desktop ports, exposed firewall web consoles and stale NAT mappings. A careless commit can be found within minutes. Below are the five management failures I'd check first, along with the fixes the source material recommends for each.
Mistake 1: Permissive rules, rule bloat and shadowed policies
Almost every experienced network engineer has watched this one start. An ERP upgrade breaks at 11:30 on a Sunday night. Leadership wants service back before Monday, so an exhausted administrator inserts a temporary diagnostic rule near the top of the table: source any, destination the server subnet, service any, action allow. The application comes back, everyone relaxes, and nobody returns on Tuesday to narrow it to specific ports and application signatures.
Repeat that across five years of projects and the rulebase fills with redundant, conflicting and shadowed entries. Because firewalls evaluate rules top-down, a broad allow sitting high in the list can match traffic before a granular deny further down ever gets a look. The result is a shadowed rule that looks like protection on the dashboard and does nothing in practice. Unrestricted outbound rules add a second problem: a compromised workstation can open a reverse shell on any port to a command-and-control server.
The fix: Apply least privilege to both inbound and outbound flows. Move from port-only rules toward application and user identity controls, attach expiry dates to every temporary rule, and remove any policy with zero hits over a rolling 90-day window.
Mistake 2: Flat internal networks
The classic castle-and-moat design put a hardened perimeter firewall on the internet edge and let VLANs route freely inside the building. That model struggles with spear-phishing, stolen OAuth tokens and compromised contractor laptops. A hard shell over a soft interior is a gift to ransomware operators.
If nothing inside is inspecting east-west traffic, a single infected printer, badge reader or marketing laptop can see domain controllers, SQL servers and backup repositories. Attackers lean on native administration protocols such as SMB, WMI and RDP to spread quickly, turning one workstation infection into an enterprise-wide encryption event before the SOC has reviewed the first alert.
The fix: Move toward a zero trust model built on network micro-segmentation. Route inter-VLAN traffic through internal segmentation firewalls or distributed workload firewalls, and isolate crown-jewel systems, immutable backups, operational technology and guest Wi-Fi into tightly bounded zones with identity checks and IPS inspection on every east-west flow.
Mistake 3: Exposed management planes and unpatched edge appliances
It's an uncomfortable irony when the firewall becomes the way in. Over roughly the past three years, espionage groups and initial access brokers have pushed hard at perimeter appliances, going after command injection, authentication bypass and memory handling flaws in edge firewalls and SSL VPN gateways. These devices run stripped-down operating systems that can't host conventional EDR agents, which makes them attractive, quiet footholds.
The exposure gets worse when HTTPS management, SSH or SNMP is bound to a public WAN interface for convenience. Even without an active exploit, internet-facing login pages attract password spraying and credential stuffing, especially against local admin accounts without multi-factor authentication.
The fix: Turn off HTTPS, SSH, ping and SNMP management on untrusted interfaces. Put administration on a dedicated out-of-band network reachable only through hardened jump hosts with hardware MFA. Run active-passive HA so firmware updates don't take the network down, and aim to apply critical vendor security advisories within 48 hours of release, which the source frames as part of ongoing attack surface management.
Mistake 4: Leaving encrypted traffic uninspected
Most web traffic now travels over TLS 1.2 or 1.3, and malware authors know it. Ransomware droppers, phishing kits and exfiltration endpoints are routinely hosted behind legitimate CDN providers with valid certificates. Buy a next-generation firewall with sandboxing, anti-malware and data loss prevention, then leave decryption off, and you've paid for a lot of features that can't see the traffic that matters.
Teams usually hold off for two reasons. They worry that undersized firewall CPUs will drag throughput down, or that decryption will break certificate pinning in banking, healthcare and developer tools. Still, without decryption, inline IPS and malware engines see only encrypted traffic moving over port 443.
The fix: Size hardware against the vendor's published TLS inspection throughput rather than cleartext numbers. Distribute your internal subordinate root certificate to managed endpoints through Group Policy or MDM, apply inbound inspection to public DMZ servers, and create bypass categories only for healthcare, financial and pinned software-update domains. Decrypt everything else, especially uncategorized, newly registered and high-risk sites.
Mistake 5: Unwatched logs, alert fatigue and undocumented change
A firewall isn't only a blocker. It's one of the highest-fidelity sensors you own. Repeated denied outbound connections from a database server, a sudden jump in DNS tunnelling queries or an off-hours admin login are the kinds of early signals that precede a real intrusion. Many environments still keep logs on a small onboard disk that overwrites itself every two days, or forward millions of informational events to a SIEM with no correlation rules behind them.
Configuration drift makes it worse. When engineers edit devices directly instead of pushing templates through a central orchestrator, peer review disappears. Unauthorised NAT changes slip through, rules multiply across cloud security groups and on-premises appliances, and restores fail because the backup config no longer matches production.
The fix: Stream traffic, threat, decryption and configuration audit logs in real time to an immutable SIEM or SOAR platform. Set high-priority alerts for admin logins, rule changes and internal port scans. Use network security policy management tooling to simulate rule impact before commits, require peer-reviewed change tickets, and score drift continuously against CIS and NIST benchmarks.
Quarterly hardening checklist
Run this audit every 90 days to confirm that physical, virtual and cloud firewalls still look the way you think they do:
[ ] 1. ZERO-HIT RULE PURGE: Disable and archive rules with 0 packet hits over 90 days.
[ ] 2. ELIMINATE ANY-ANY: Refactor legacy port rules into Layer-7 App-ID + User-ID policies.
[ ] 3. LOCK DOWN MANAGEMENT: Verify 0 public WAN exposure on ports 22, 443, 8443, and 161.
[ ] 4. PATCH & HA SYNC CHECK: Confirm latest recommended PSIRT firmware + test HA failover.
[ ] 5. EGRESS & GEO-BLOCKING: Enforce strict outbound port controls + block embargoed ASNs.
[ ] 6. VALIDATE SIEM ALERTS: Trigger a test admin change and verify real-time SOC alerting.
Questions teams ask most
How often should a ruleset be reviewed? PCI DSS calls for firewall rule reviews at least every six months. Security-mature teams tend to go quarterly and pair that with continuous monitoring, so shadowed, orphaned or overly broad rules get caught as they appear.
What's a shadowed rule? It's a rule that never fires because an earlier, broader rule matches the same traffic first. An any-any allow near the top is the classic example, and it leaves the stricter deny lower down completely inactive.
Do zero trust and cloud make firewalls obsolete? No, but they change where the firewall lives. Capabilities spread across data centres, cloud virtual appliances, container meshes and cloud-delivered edges, ideally under one policy model.
Why does outbound filtering matter as much as inbound? Phishing payloads and trojans call out from inside the network to fetch encryption keys and push data out. Strict egress rules cut off unapproved ports, unsanctioned cloud storage uploads and command-and-control callbacks before the damage spreads.
Where to start
Attackers don't need elaborate techniques when stale rules, open internal lanes, exposed management ports, uninspected tunnels and silent logs are already in place. The brand on the rack matters far less than the habits your team keeps between projects. My advice is to start with the checklist this quarter: prune zero-hit rules, close management exposure on the WAN, and confirm that someone actually receives the alerts. Those three steps tend to surface the worst problems fastest.


